
v2.8.9
Safer Team Access, Reseller Mailbox Plans, and Smarter Cloudflare Enterprise
xCloud v2.8.9 makes team access easier to maintain, opens Mailbox plans to white-label resellers, lets customers claim credit for server plans they bought but did not deploy, and expands Cloudflare Enterprise automation. It also makes site deletion safer and more recoverable, improves billing integrity, and fixes long-standing issues across Git setup, backups, WordPress monitoring, Node.js, OpenLiteSpeed, and DeepSeek Harness.
Release at a Glance
- 7 new customer-facing capabilities
- 6 safety and usability improvements
- 13 customer-impacting fixes
🔥 New Features
Team access that keeps up as you grow
Sharing your infrastructure with teammates is simpler and safer. When you invite someone, choose whether they can reach all your servers and sites, only the ones you pick, or the ones you pick plus anything you add later — so new servers and sites are shared automatically, with no need to re-invite. You can also keep a member’s permissions in step with their role, so eligible new features are granted automatically (never above their role). Sensitive actions like command execution and Magic Login still require your explicit approval.
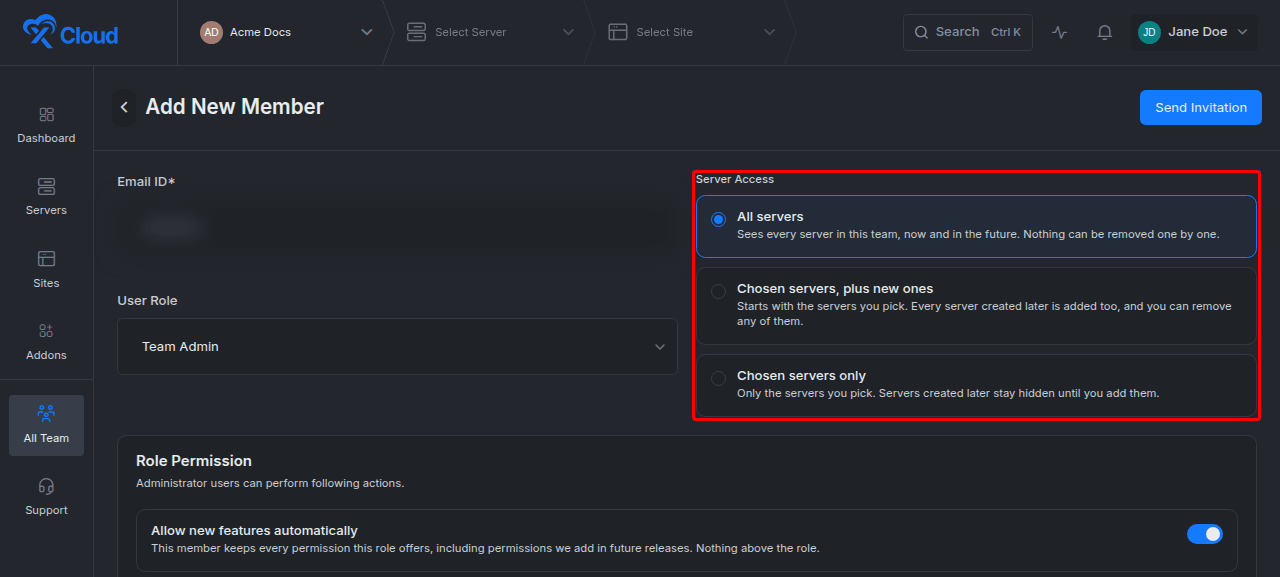
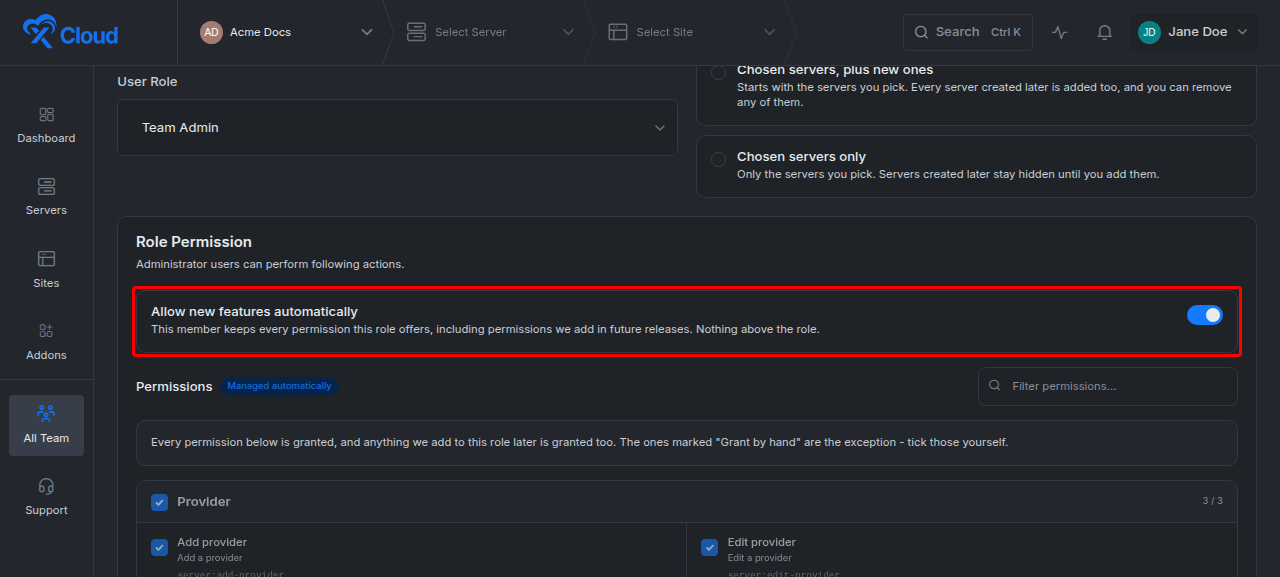
Full walkthrough: How to manage teams, roles, and permissions.
White-label Mailbox plan reselling
Resellers can now publish paid Mailbox plans under their own brand, with a custom plan name, SKU, and selling price. Plans become available to clients after they are activated and published. The free 100 MB Mailbox plan is not resellable.
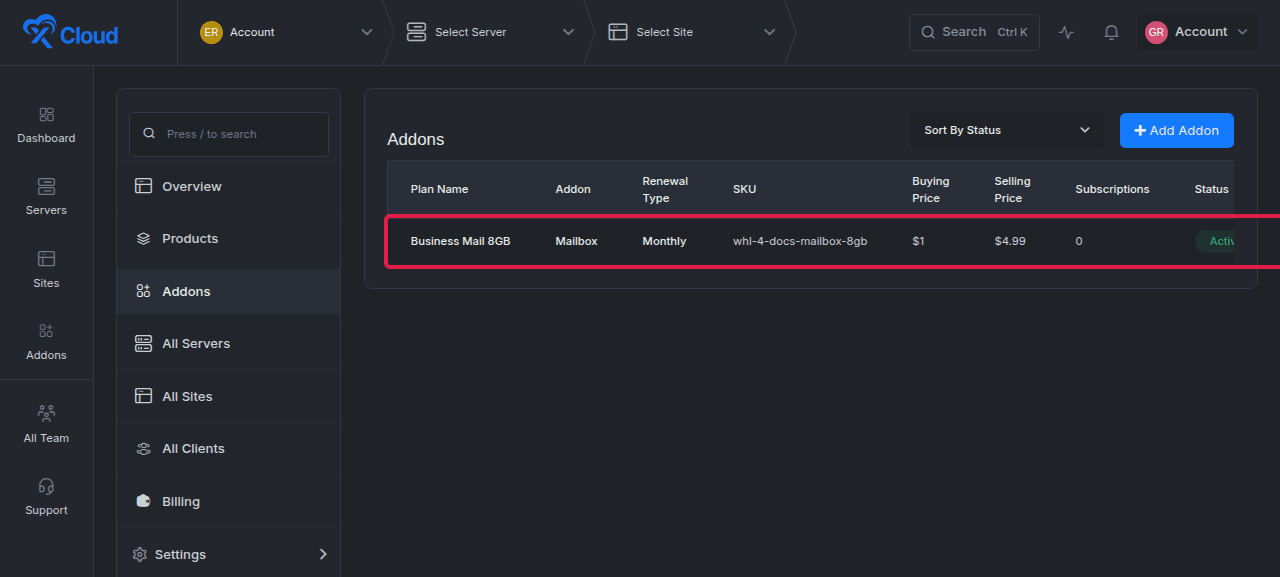
Full walkthrough: How to create and sell reseller MailBox plans.
Account Credit for unused server purchases
Customers who used “purchase now, set up later” can claim eligible unused server units as Account Credit. Each unused unit in a multi-unit purchase can be claimed separately, and the eligible credit and any applicable payout fee are shown before confirmation.
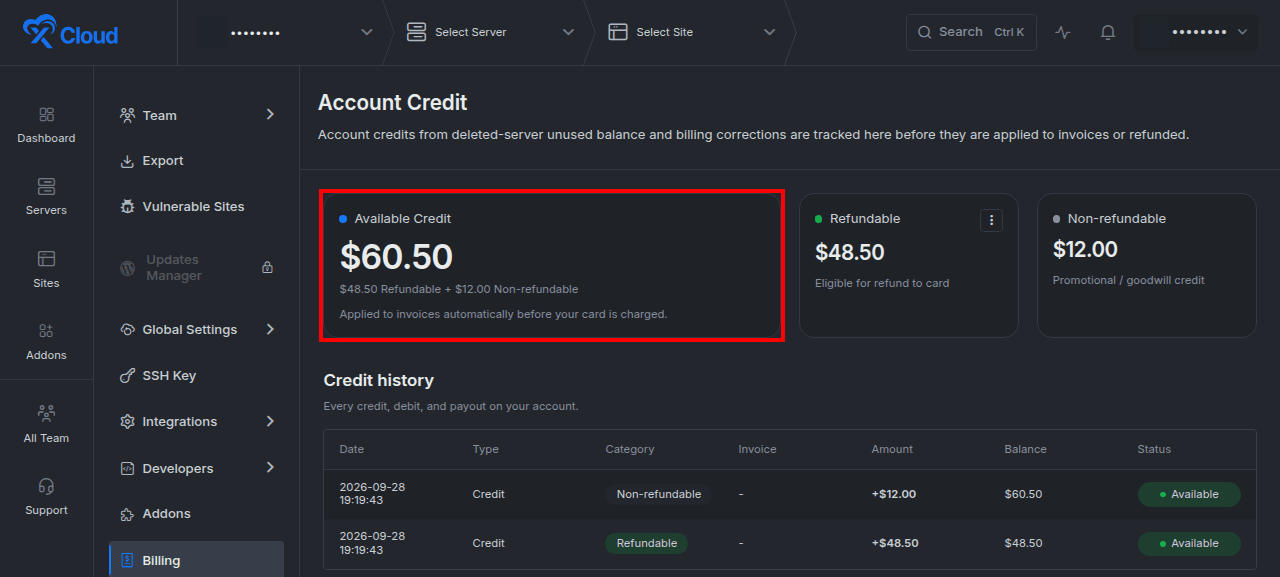
Full details: xCloud refund policy and Account Credit.
Cloudflare Enterprise auto-purge webhook
External domains and non-WordPress sites can now automatically purge only the URLs changed by a deployment. Each domain gets a secret that can be created, copied once, tested, rotated, or disabled.
Learn more: Use Cloudflare Enterprise for external domains.
Expanded Cloudflare Enterprise API
The Enterprise API now supports per-domain edge TTL settings, tenant-safe WAF rule visibility, and opaque external client references for integrations.
Reference: xCloud API documentation.
Provider-aware apex DNS guidance
xCloud now prioritizes apex DNS records supported by the customer’s DNS provider, while keeping domain ownership verification ahead of edge cutover.
Learn more: Using xCloud with Cloudflare for DNS management.
Editable support-ticket access
Customers can update SSH permission, Magic Login permission, and access validity after opening a support ticket. Support staff cannot grant themselves access.
Learn more: Access the built-in Support Portal.
✨ Improvements
- Site deletion is collision-safe, stuck deletions reach a clear failed state, and the Try Again action works.
- Cloudflare Enterprise WordPress purge credentials can be rotated, callbacks are rate-limited, staging clones receive a separate purge identity, and the plugin can be updated from its Cloudflare Enterprise page.
- Incremental backup failures now identify the database object that failed.
- Exhausted package capacity now shows a visible validation message instead of a blank failure.
- Failed self-managed server deletion now provides a usable delete and retry path.
- The Delete Local Backups option is restored during site deletion.
🐛 Bug Fixes
- Git setup no longer remains stuck on “Setup in progress”; stale setups become retryable.
- Run & Debug no longer removes the active custom Nginx configuration when validation fails.
- Cloudflare Enterprise WordPress auto-purge now clears changed URLs instead of purging the entire site.
- DeepSeek Harness provisioning no longer crash-loops because of drifting dependencies.
- Server resizes no longer renew the previous tier from stale billing chains.
- Site Security Pro now blocks duplicate purchases for the same domain.
- Package renewals now complete correctly after asynchronous payment.
- WordPress fatal-error alerts ignore stale and unrelated log entries.
- Large broken-link scans report progress in bounded batches.
- OpenLiteSpeed redirect-only domain groups no longer become the server-wide catch-all.
- Node.js and SSR sites regenerate their PM2 configuration after the start command changes.
- Sites remain assigned after Mail Delivery cancellation.
- Package capacity errors now appear inline.