

Fix MCP OAuth Connection Failures on OpenLiteSpeed Sites
Updated November 8, 2026 · 4 min read
If you run a WordPress MCP server on your own site, such as the Novamira plugin, and the site is hosted on an OpenLiteSpeed (OLS) server, AI clients that sign in over OAuth (Claude Desktop, Claude Code and similar) could fail to connect. A permanent fix is live: new OLS sites work out of the box, and existing OLS sites are fixed by regenerating the OLS config and toggling the firewall, as described below.
This is specific to an MCP server running on your WordPress site. It does not affect xCloud’s own MCP at app.xcloud.host, which is served by xCloud and unaffected by your site’s config.
Symptoms
On an OpenLiteSpeed site, the OAuth sign-in from an AI client fails in one of two ways:
- OAuth discovery returns a 404. The client’s request to
/.well-known/oauth-authorization-serveror/.well-known/oauth-protected-resourceon your site returns a LiteSpeed 404 page instead of reaching WordPress, so the client never finds the authorization server. - The authorize step returns a 403. When you approve the connection on your site’s sign-in page, you see a 403 Forbidden error from the firewall instead of being sent back to your AI app.
Application-password connections are not affected.
What caused it
- Your site’s OpenLiteSpeed settings answered every request to the
/.well-known/folder before WordPress could, so the AI client’s sign-in check got a “page not found” error. - The built-in 7G/8G firewall blocked the address your AI app uses to finish signing in on your computer, so the sign-in page showed a 403 Forbidden error.
Fix an existing OpenLiteSpeed site
New OLS sites already include the fix. For an existing OLS site, apply it in two steps from the xCloud dashboard.
Step 1: Regenerate the OpenLiteSpeed config
Open the site and go to Site Settings. In the Rescue Site card, turn on Regenerate OpenLiteSpeed Configuration, then click Run Now. In the Rescue Site dialog that asks if you are sure, click Yes, Run Now. You see the message Site rescue job has been initiated. This only means the rescue has started. Wait a minute or two for it to finish. To check, open the site’s Events page and look for the Regenerate OpenLiteSpeed Config event.
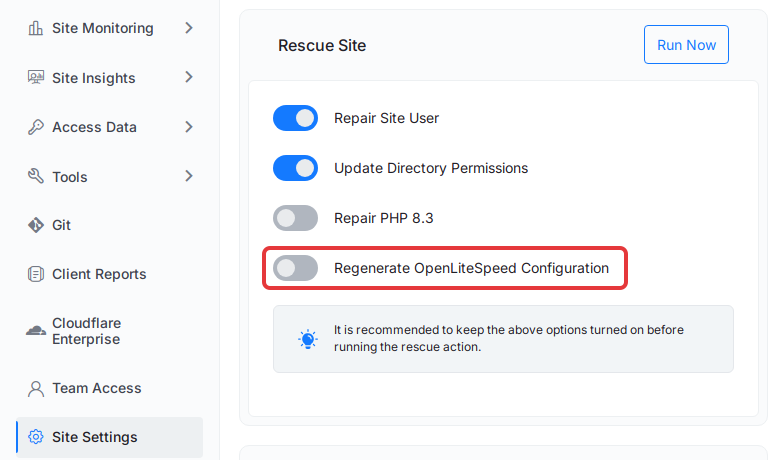
Your AI app can now find your site’s sign-in page. Your SSL certificate keeps working, and private files stay blocked.
Step 2: Turn the 7G or 8G firewall off and on
If the 7G or 8G firewall is on for the site, go to Security → Overview & Firewall. In the Security Settings card, under Firewall rules, turn off the firewall that is on (7G Firewall or 8G Firewall) and click Save Settings. Then turn it back on and click Save Settings again.
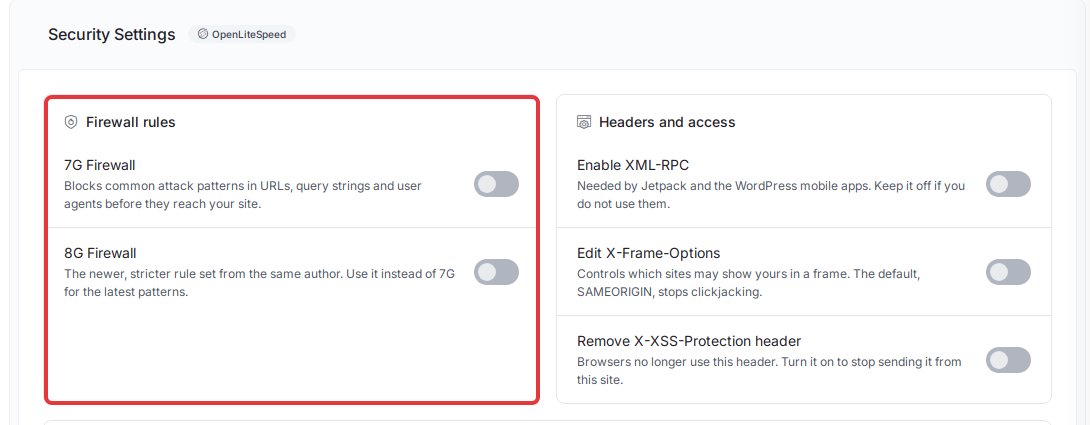
The firewall is reinstalled with the fix that lets the AI app’s sign-in finish on your computer. Switching between 7G and 8G, or turning one off and on, always leaves just one firewall active, with no old 7G rules left next to 8G.
When the rescue from Step 1 has finished (and you have finished Step 2, if you use a firewall), reconnect the AI client and complete the sign-in to your site.
What the fix changes
- Sign-in check reaches WordPress. Your AI app can now find your site’s sign-in page. Your SSL certificate still renews as before, and hidden files like
.envand.gitstay blocked. - Firewall exception for AI sign-in. The 7G and 8G firewalls now let your AI app finish signing in on your computer, but only on the WordPress sign-in and authorization pages. Every other firewall rule still applies.
- Clean firewall state. Switching between 7G and 8G, or turning one off and on, always leaves just one firewall active.
Nginx sites on the 7G firewall
On Nginx sites, the 7G Firewall now lets your AI app finish signing in too. If sign-in on an older Nginx site still fails with a 403 “Forbidden” error, turn the firewall off and on: open Security → Overview & Firewall. In the Security Settings card, turn 7G Firewall off and click Save Settings, then turn it back on and click Save Settings again.
Still failing after the fix? Check these
A security plugin hides or locks wp-admin
If OAuth discovery now returns JSON but the authorize step still returns a 403 with a message such as “This has been disabled”, the block is coming from a WordPress security plugin rather than the server. Solid Security’s Hide Backend setting, for example, returns 403 for logged-out requests to wp-admin, which includes the OAuth authorization screen. Turn that feature off (or add the authorization URL to its allow list), then retry the sign-in.
AI Bot Blocker blocks assistants acting for a user
AI Bot Blocker allows AI assistants that act for a person, such as Claude-User and ChatGPT-User, by default. A Claude or ChatGPT connector calling your site’s MCP server is one of them. If you turned on Also block AI assistants acting for a user, those requests are blocked. Turn that option off on the AI Bot Blocker card, then reconnect.
The site is behind Cloudflare
xCloud’s Cloudflare WAF rules do not block the WordPress sign-in and authorization pages or the OAuth discovery addresses. Allow Good Bots + ACME/Let’s Encrypt Validation makes xCloud’s other Cloudflare rules ignore known good bots, such as search engine crawlers, and Let’s Encrypt certificate checks. It blocks nothing. The other rules cover sensitive files, wp-config.php, xmlrpc.php and author enumeration. If a request is still blocked at Cloudflare, it comes from a setting on your Cloudflare zone itself: check the zone’s security events in Cloudflare to find the rule.
Related docs
- Connect AI clients to WordPress with Novamira on xCloud
- How to Configure Firewall Management in xCloud
- Enable the 8G Firewall in xCloud
- Enable AI Bot Blocker in xCloud
- How to Enable Cloudflare WAF Rules in xCloud
If you run into any issues with the MCP OAuth connection, feel free to reach out to our support team.
Technical note
After the fix, only /.well-known/acme-challenge/ (used to issue and renew SSL certificates) is answered directly by OpenLiteSpeed. Every other /.well-known/ request goes to WordPress.
Frequently asked questions
What exactly is affected?
Signing an AI client in over OAuth to a WordPress MCP server that runs on your own site, for example the Novamira plugin, when that WordPress site is hosted on an xCloud OpenLiteSpeed (OLS) server. It is not about connecting xCloud’s own MCP at app.xcloud.host, which is unaffected. Application-password connections are also not affected.
Do new OpenLiteSpeed sites need this fix?
No. New OLS sites created after the permanent fix shipped work out of the box. This procedure is only for existing OLS sites created before the fix.
Is regenerating the OLS config or toggling the firewall safe?
Yes. Your SSL certificate still renews as before, and switching between 7G and 8G, or turning one off and on, always leaves just one firewall active. If support applied a temporary fix to your site, the official one replaces it.
Does xCloud’s Allow Good Bots Cloudflare rule need to include my AI client?
No. Allow Good Bots makes xCloud’s other Cloudflare rules ignore known good bots, such as search engine crawlers, and Let’s Encrypt certificate checks. It blocks nothing. None of xCloud’s Cloudflare rules target the OAuth sign-in pages either, so an AI client does not need to be on it. If a request is still blocked at Cloudflare, check your Cloudflare zone’s own security events for the rule that stopped it.