

How To Add Custom Security Headers in xCloud
Updated November 3, 2026 · 3 min read
Security headers are essential for protecting your websites from common web vulnerabilities by controlling how browsers behave. This guide will walk you through the correct way to add custom security headers in xCloud, covering both OpenLiteSpeed (OLS) and NGINX web servers. For an overview of what it does and which plans include it, see the security headers feature page.
In xCloud, directly editing the main server configuration files (like vhconf.conf) is not recommended, as these files are managed by the control panel and can be overwritten automatically when changes are made via the UI.
Easiest way on WordPress sites: open the site and go to Tools → Site Rules. Header rules there come with presets for Strict-Transport-Security, Referrer-Policy, Permissions-Policy, Content-Security-Policy, X-Content-Type-Options and X-Frame-Options, and work on both Nginx and OpenLiteSpeed without SSH. See How to Create and Manage Site Rules. Use the manual methods below for other site types or for headers the presets do not cover.
Only X-Frame-Options? On Nginx and OpenLiteSpeed alike, go to Security → Overview & Firewall, turn on Edit X-Frame-Options in the Headers and access group of the Security Settings card, enter the value (the default is SAMEORIGIN; DENY, ALLOWALL and ALLOW-FROM with one or more URLs are also accepted) and click Save Settings.
Remove the X-XSS-Protection header
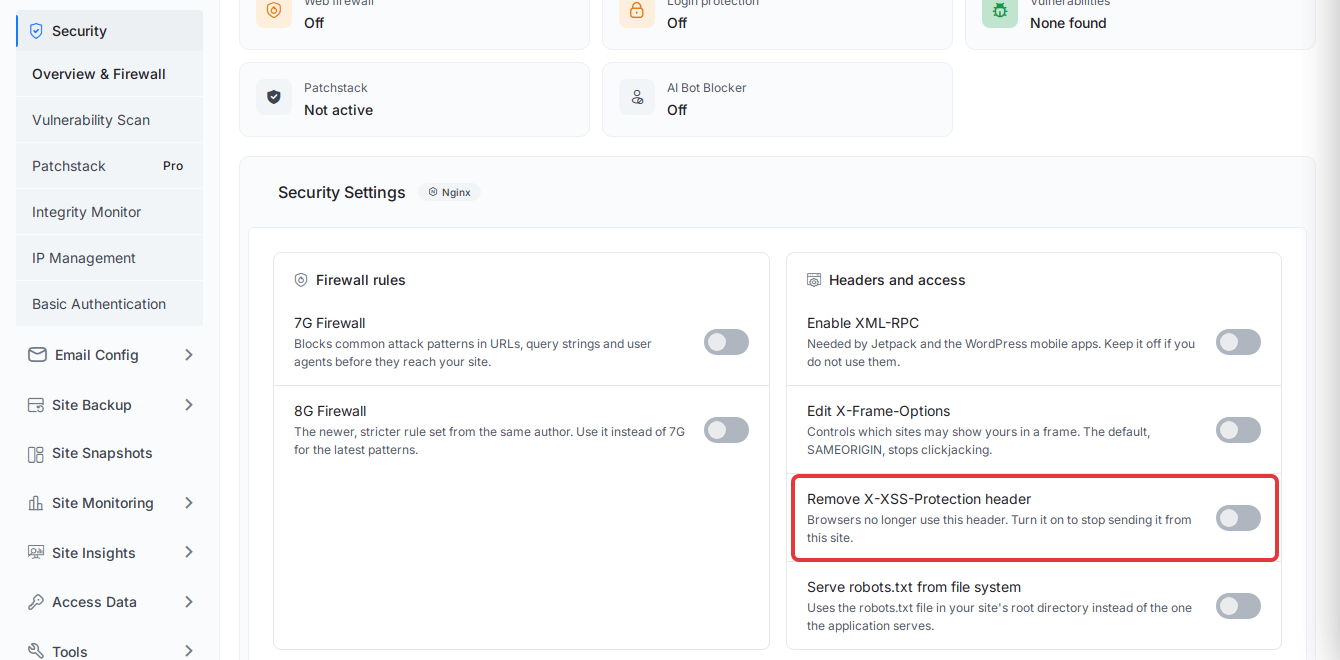
Turn on Remove X-XSS-Protection header to stop a site sending this header. Current browsers no longer use it, and a security scan can flag it. Free on every plan. xCloud adds it to Nginx and OpenLiteSpeed sites. The switch is off by default, so a site keeps the header until you turn the switch on.
The switch removes the header from the site’s PHP pages and static files. On Nginx, images and CSS files never send this header. It covers that one site, and the other security headers stay. It does not appear for Node.js or Docker sites. One-Click App sites run on Docker, so they don’t have this switch.
Removing this header on Nginx? On Nginx, a Site Rule set to Unset doesn’t remove this header in our test, so use this switch.
Step 1: Find the switch
These steps cover sites with a Security menu, such as WordPress, PHP, Laravel and Mautic sites. Open the site and go to Security → Overview & Firewall. In the Security Settings card, find Remove X-XSS-Protection header in the Headers and access group.
Step 2: Turn it on and save
Turn on the switch, then click Save Settings. xCloud applies the change to your site. You see Nginx Config updated successfully or OpenLiteSpeed Config updated successfully.
Step 3: Check the result
Run these commands from your own computer, using your domain. First, confirm that a page and a .txt file both answer. Replace license.txt with a .txt file that exists on your site:
curl -sI https://example.com/ | head -1
curl -sI https://example.com/license.txt | head -1
The first line of each reply should show 200, such as HTTP/2 200. If it shows another number, or you see nothing, this check can’t tell you the result. If the number is 301 or 302, your address redirects, so use the address it redirects to. If it is 401, turn off password protection for the site, then run the check again.
Once both show 200, check for the header at the same two addresses:
curl -sI https://example.com/ | grep -i x-xss-protection
curl -sI https://example.com/license.txt | grep -i x-xss-protection
With the switch off, each command prints a line reading x-xss-protection: 1; mode=block. The capital letters may differ. With the switch on, neither command prints anything, which means the site no longer sends the header. If a line still appears, a plugin, your app or a CDN such as Cloudflare may be adding the header or serving a saved copy. Check those, clear the CDN cache and run the check again. To send it again, turn off the switch and click Save Settings.
If you can’t see the switch
If the menu item is missing or the switch is greyed out, your team role doesn’t allow this change. Ask your team admin.
The Headers and access group is also hidden while Disable Nginx Config Regeneration or Disable OpenLiteSpeed Config Regeneration is on, because you manage the config files yourself. To use the switch:
- On the same page, find the setting in the Config management group of the Security Settings card.
- Turn it off.
- In the confirmation that opens, click Yes, Enable.
The Headers and access group comes back, with Remove X-XSS-Protection header in it. Once you turn the setting off, xCloud rewrites these config files when you save, so changes you made by hand in them are replaced. Copy your changes first.
Add Custom Security Headers on OLS Servers in xCloud
Step 1: SSH Into Your Server
Before making any changes, SSH into your OLS server.
Step 2: Use the vhconf.server.conf Config File
Use the following file to define your custom HTTP security headers:
/usr/local/lsws/conf/vhosts/example.com/vhconf.server.confThis file is not overwritten by the xCloud panel and is ideal for persisting manual changes such as custom headers.
Step 3: Add Security Headers
To add custom security headers, update vhconf.server.conf with the following block:
  context / {
extraHeaders <<<END_extraHeaders
set Strict-Transport-Security "max-age=31536000; includeSubDomains; preload";
set Referrer-Policy "strict-origin-when-cross-origin";
set Content-Security-Policy "upgrade-insecure-requests";
set Permissions-Policy "accelerometer=(), autoplay=(self https://www.youtube.com https://www.google.com https://www.facebook.com https://www.instagram.com https://platform.twitter.com https://player.vimeo.com https://www.linkedin.com https://js.hsforms.net), camera=self, cross-origin-isolated=(), display-capture=self, encrypted-media=(self https://www.youtube.com https://www.facebook.com https://www.instagram.com https://player.vimeo.com), fullscreen=(self https://www.youtube.com https://www.vimeo.com https://player.vimeo.com https://www.instagram.com https://www.facebook.com https://platform.twitter.com https://www.linkedin.com), geolocation=(self https://www.google.com), gyroscope=(), keyboard-map=(), magnetometer=(), microphone=self, midi=(), payment=(self https://connect.stripe.com https://checkout.paypal.com https://js.squareup.com), picture-in-picture=(self https://www.youtube.com https://www.vimeo.com https://player.vimeo.com https://www.instagram.com https://www.facebook.com), publickey-credentials-get=self, screen-wake-lock=(), usb=(), web-share=(self https://www.youtube.com https://www.facebook.com https://www.instagram.com https://platform.twitter.com https://www.linkedin.com), xr-spatial-tracking=(), clipboard-write=self, clipboard-read=self, interest-cohort=()";
END_extraHeaders
}
Step 4: Apply the Configuration
After updating the configuration, restart LiteSpeed to apply the changes:
systemctl restart lsws && killall -9 lsphpAdd Custom Security Headers on NGINX Servers in xCloud
For NGINX-based xCloud servers, you can add custom security headers right from the xCloud Dashboard.
Read this documentation for more information about custom NGINX:
👉How To Configure Custom NGINX In xCloud?
📌 Notes
-
Do not edit vhconf.conf directly – it’s automatically regenerated by the xCloud panel.
-
Use vhconf.server.conf on OLS servers to retain customizations.
-
Always restart LiteSpeed or NGINX after making changes for them to take effect.
Adding custom security headers is a crucial step in hardening your website against common threats such as cross-site scripting, clickjacking, and data injection attacks. It’s important to apply these headers in a way that aligns with the platform’s configuration management to avoid losing changes during updates.
Frequently asked questions
Is my site less safe without the X-XSS-Protection header?
Current browsers no longer use this header, so removing it does not take away a protection they apply. The site’s other security headers stay in place.
Does the switch change all my sites?
No. It covers one site. Turn it on for each site that should stop sending the header.
How do I get the X-XSS-Protection header back?
Turn off Remove X-XSS-Protection header and click Save Settings. The site sends the header again.
Still stuck? Contact our support team for any of your queries.