

How Automated Security Updates and Auto Reboot Work in xCloud
Updated November 5, 2026 · 7 min read
xCloud installs security updates on every server it provisions and can reboot the server for you when an update needs it. This guide explains exactly what those two features do, which packages they cover, and how to check a specific package yourself. For the click-by-click steps to turn on Automatic Reboot, see Keep Your Server up to Date with Automated Security Updates. For an overview of what it does and which plans include it, see the automated security updates feature page.
In one paragraph: xCloud configures Ubuntu unattended upgrades to install eligible updates from the repositories enabled and entitled on your server. Some updates require a reboot; xCloud can notify you or reboot automatically at your chosen time. Automatic Reboot does not add repository subscriptions or extended-security entitlement.
How updates reach your server
Every xCloud server runs Ubuntu’s unattended-upgrades package, which xCloud installs and configures during provisioning. By default it installs updates from Ubuntu’s security repositories, and cleans up afterwards. This covers the operating system kernel and the packages that come from Ubuntu, such as OpenSSL, Ubuntu’s NGINX package and system libraries. NGINX from nginx.org and OpenLiteSpeed are not updated automatically.
An update is “available” to unattended-upgrades only when an allowed repository offers an installable, newer version of an installed package. That repository boundary is the important detail in the rest of this guide.
Managed Service Updates
xCloud installs PHP (LiteSpeed PHP on OpenLiteSpeed servers), MySQL 8.4, MariaDB 11.8, Redis and Node.js from their own repositories, not from Ubuntu. Ubuntu’s security updates therefore do not install their patch releases, including PHP and Node.js security releases. You have two ways to keep them patched:
- Automatically: on the server’s Security Update page, turn on Managed Service Updates and pick an update time. It is off by default. The server then installs updates from those repositories once a day, keeping each service on the series it already runs, and its daily Ubuntu security run moves to the same time. See Keep Your Server up to Date with Automated Security Updates.
- Manually: for PHP, go to Management → Manage PHP, click Scan Patch, then Update to on the version that has a patch. See Install PHP Security Patches. For Node.js, see How to Update Node.js on Your xCloud Server.
Node.js patches install only when your server’s Node.js version, such as 22, matches the version of the package source xCloud set up for it. The Node.js row tells you if it doesn’t. After one installs, only the running PM2 apps still using the old Node.js version are reloaded. Apps that run from a release folder stay on the old Node.js until their next deploy or settings update. The Components on this server list on the same page shows each service, how it gets updated and why a service is not included, such as Docker, because a Docker upgrade restarts every container.
On Ubuntu 22.04 or later, MySQL 8.0 comes from Ubuntu, so Ubuntu’s security updates already cover it.
MariaDB 10.x is not covered by Managed Service Updates. Until the AL-2026-144 patch is applied, it gets its fixes through Ubuntu security updates, and its row reads Ubuntu security updates. The patch moves the server to the MariaDB repository, which Ubuntu’s updates do not reach, so from then on its row reads Not included · Not updated automatically. In both states, check its badge under Components on this server. If it stays on Update pending, contact support.
On a MariaDB 11 server, only MariaDB 11.8 is updated automatically. A server on another MariaDB 11 version, such as 11.4, shows MariaDB as Not included with the note Only MariaDB 11.8 is updated automatically.
For the MariaDB security advisory AL-2026-144, xCloud patches affected MariaDB servers itself, with a Patch Date and an ‘Update now’ button on the Security Update page. See Apply the MariaDB Security Patch (AL-2026-144) in xCloud.
What Automatic Reboot does
Some updates, most often kernel updates, only take effect after a reboot. When one is installed, Ubuntu creates the file /var/run/reboot-required. xCloud’s monitoring notices that file and:
- shows a reboot required notice on the server in your dashboard, and
- sends you an email notification.
The notice appears at the top of the server’s pages and says the server requires a reboot. If Automatic Reboot is on, it says instead that the server will automatically update and reboot at your chosen time, in the server’s timezone, and that you can also reboot now. It gives you three choices:
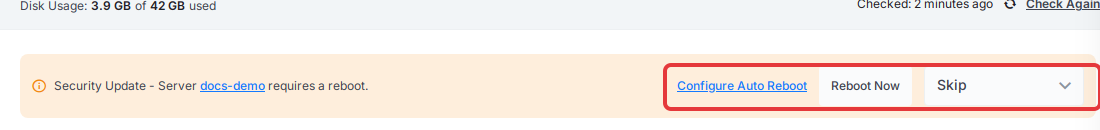
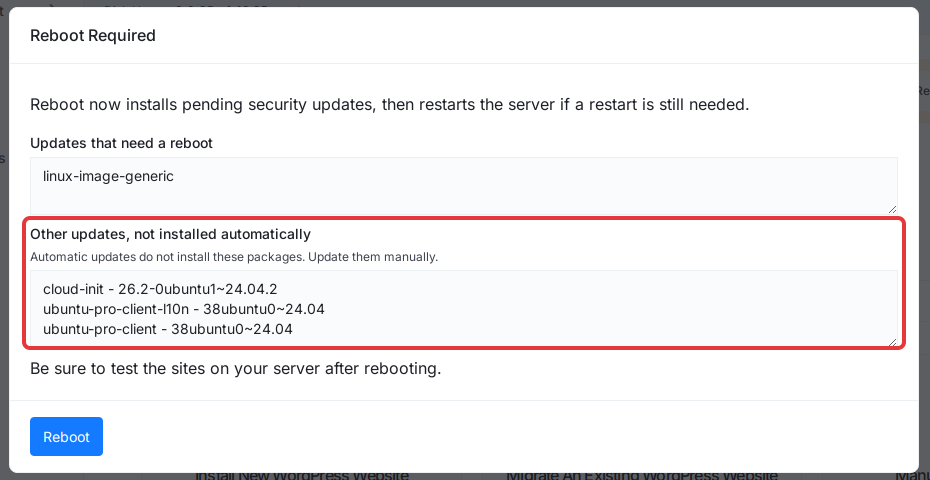
- Reboot Now opens a Reboot Required summary of the waiting packages, grouped under Updates that need a reboot, Installed on the next automatic run and Other updates, not installed automatically (only the groups that have packages show; on some older servers, all waiting packages show in one Updates Available list instead). Click Reboot to confirm: xCloud installs the pending security updates first, then restarts the server if a restart is still needed. Test your sites afterwards.
- Configure Auto Reboot opens the server’s Security Update page, where you turn on Automatic Reboot.
- Skip hides the notice for 3, 7 or 30 days, or for good with Always Skip.
The notice does not show on a server created in the last 12 hours. If the To-Do Center is on for your team, its Security updates are waiting card takes the notice’s place.
The Automatic Reboot setting on the server’s Security Update page does two things:
- It turns Ubuntu’s
Unattended-Upgrade::Automatic-Rebootoption on or off. - When on, it sets
Unattended-Upgrade::Automatic-Reboot-Timeto the time you pick, in the server’s configured timezone.
The server then reboots at that time only if a reboot is currently required. If nothing needs a reboot, the setting does nothing that day. Pick a low-traffic window. Your sites are briefly unavailable during the reboot, so test them afterwards.
Updates the automatic run does not install
Not every pending package update is a security update the daily run will install. The server’s Security Update page lists those under Other updates, not installed automatically, with the package name and version. The card says: Automatic updates do not install these packages. Update them manually.
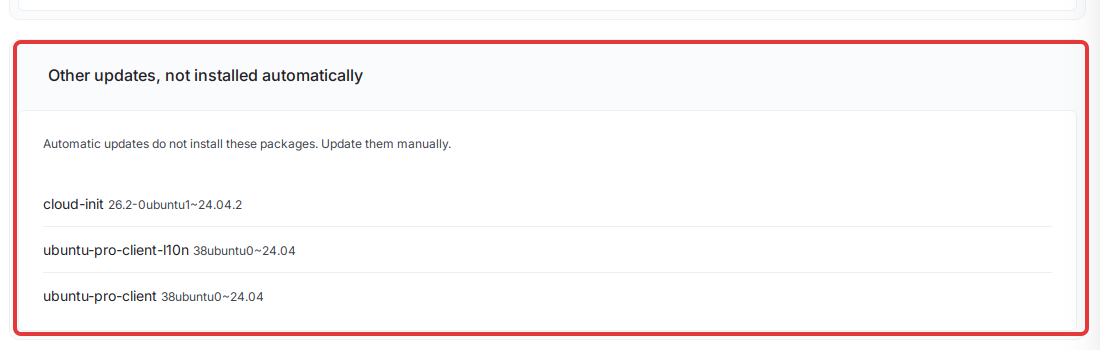
Some rows give a reason. Held back by the last update run, checked again within a day means the last automatic run tried the update and left it. xCloud checks it again within a day. If a newer version of that package comes out, xCloud treats it as a new update.
Updates that only Ubuntu Pro can install (ESM) are left out of this list and out of the To-Do Center, because a server without Ubuntu Pro cannot download them. See Ubuntu main, universe and ESM Apps.
These packages do not keep the Security updates are waiting card open in the To-Do Center, and they do not make its Fix fail. That card does not count updates listed under Other updates, not installed automatically.
What Automatic Reboot does not do
Automatic Reboot handles the last stage of the update lifecycle: after an eligible update is installed and Ubuntu marks a reboot as required, xCloud can schedule that reboot. It does not:
- reboot the server on a schedule regardless of need;
- install updates on its own schedule. The one exception: saving the page with Automatic Reboot on and Managed Service Updates off installs pending Ubuntu security updates right away.
- attach the server to Ubuntu Pro or grant any Canonical entitlement;
- enable the ESM Apps repository;
- turn a Canonical security notice into an installable package when no fixed version is offered to your server;
- guarantee that every installed package receives security maintenance under your server’s current repository entitlement.
Changing the reboot time cannot make an unavailable update installable.
Ubuntu main, universe and ESM Apps
Canonical maintains Ubuntu packages in separate streams, and this decides what unattended-upgrades can install on a server that is not attached to Ubuntu Pro:
| Repository | Who maintains security fixes | Installable on a standard xCloud server? |
|---|---|---|
main |
Canonical, for the release’s standard support period | Yes |
universe |
Community; Canonical publishes fixes through ESM Apps (part of Ubuntu Pro) where it offers coverage | Only when the fix is also published to the standard repository |
| ESM Apps / ESM Infra | Canonical, for Ubuntu Pro subscribers | No, unless the server is attached to Ubuntu Pro |
xCloud enables universe during provisioning because parts of the default stack depend on packages that live there, for example image-processing libraries such as ImageMagick that PHP’s Imagick extension needs. A package can therefore be installed from universe, appear in pro security-status --esm-apps as having a fix available, and still have no installable fixed version through the server’s standard APT configuration.
Canonical’s own references: Ubuntu Extended Security Maintenance, Canonical security documentation: ESM, and About ESM services.
Running an Ubuntu release that has left standard support has the same effect for main packages. If your server is still on Ubuntu 20.04, see how to migrate from Ubuntu 20.04 to Ubuntu 24.04.
How to check a specific package
Connect over SSH or open the web terminal and run the following. Replace PACKAGE with the package name from the security notice, for example imagemagick or libssl3.
1. Is a newer version installable?
apt-cache policy PACKAGECompare the Installed: and Candidate: lines. If they match, your enabled repositories offer nothing newer, and unattended-upgrades has nothing to install. If Candidate: is newer, the next unattended run installs it.
2. Does the fix live in ESM Apps?
pro security-status --esm-appsThis lists packages on the server that have updates in Canonical’s ESM Apps stream. A package listed here has a fix from Canonical, but on a server that is not attached to Ubuntu Pro that fix is not installable through apt.
3. Is a reboot pending?
cat /var/run/reboot-required 2>/dev/null || echo "No reboot required"If the file exists, an installed update is waiting on a reboot. Either reboot from the dashboard or let Automatic Reboot handle it at the scheduled time.
If a package you rely on has no installable fix
Keep the automated updates and Automatic Reboot enabled; they still handle everything your repositories do offer. Then send our support team the following so we can look at the specific case with you:
- the server’s Ubuntu release (
lsb_release -ds); - the package name and installed version;
- the CVE or Ubuntu Security Notice (USN) you are tracking;
- the output of
apt-cache policy PACKAGEandpro security-status --esm-apps.
Please do not enable additional third-party repositories, remove default-stack packages, or change the server’s APT sources by hand to work around a missing update. Those changes are outside what xCloud provisions and can break future updates for the whole stack.
Frequently asked questions
Is NGINX updated automatically?
It depends on where your NGINX comes from. Ubuntu’s NGINX package gets Ubuntu’s security updates automatically. NGINX from nginx.org is not updated automatically, because the extra NGINX modules xCloud builds must match the installed NGINX version. OpenLiteSpeed is not updated automatically either. The Components on this server list on the Security Update page shows which one your server has.
Why is a package listed under ‘Other updates, not installed automatically’?
The daily automatic run does not install it, so it does not count as a waiting security update. Some rows give a reason, such as ‘Held back by the last update run, checked again within a day’. Update these packages yourself if you need them.
Do automated security updates install PHP security patches?
Not by default. xCloud installs PHP from its own repositories, which Ubuntu’s security updates do not cover. Turn on ‘Managed Service Updates’ on the server’s Security Update page, or install the patch from Management → Manage PHP with Scan Patch.
Does Automatic Reboot install updates?
No. Ubuntu’s unattended-upgrades installs eligible updates on its own schedule. Automatic Reboot only controls whether the server reboots by itself when an installed update requires a reboot, and at what time. One exception: saving the page with Automatic Reboot on and Managed Service Updates off installs pending Ubuntu security updates right away.
Does Automatic Reboot restart my server every day?
No. The server reboots at the selected time only when Ubuntu has marked a reboot as required. If nothing needs a reboot, nothing happens.
Does xCloud attach my server to Ubuntu Pro or ESM Apps?
No. xCloud configures unattended-upgrades to install updates from the repositories already enabled and entitled on your server. It does not add repository subscriptions or extended-security entitlement.
Why does a package still show as vulnerable after updates and a reboot?
Usually because no fixed version is installable from the repositories your server is entitled to. Packages from Ubuntu’s universe repository receive security maintenance through Canonical’s ESM Apps stream, which is part of Ubuntu Pro. Check with apt-cache policy and pro security-status --esm-apps, then contact support with the details.
What timezone does the reboot time use?
The server’s configured timezone. See adjusting time zone settings in xCloud servers if the time you pick should follow a different region.
Related
- Keep Your Server up to Date with Automated Security Updates: turning on Automatic Reboot, step by step
- Use the To-Do Center in xCloud: the Security updates card and its Fix
- Server and Website Security with xCloud: the rest of xCloud’s security features
- How to Automate Security Updates with xCloud: the blog overview
If you run into any issues with security updates, feel free to reach out to our support team for help.